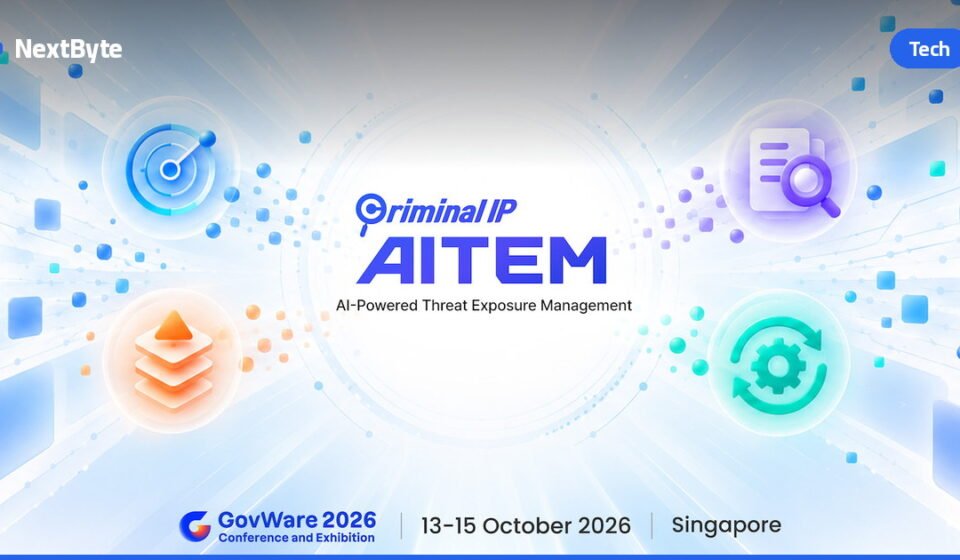

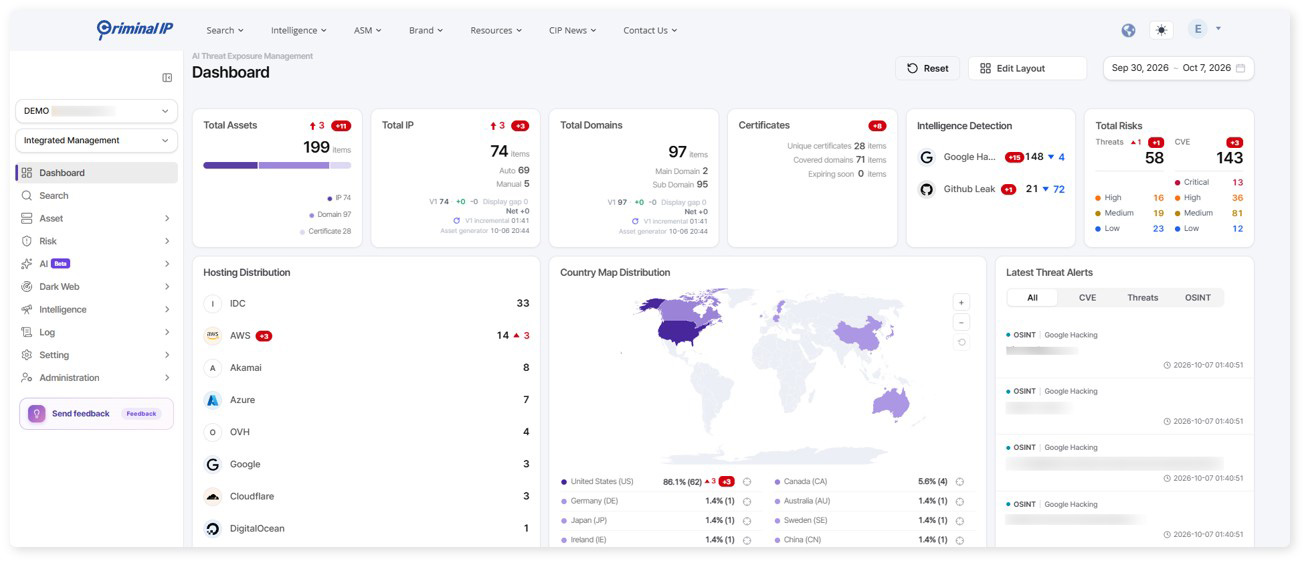
Criminal IP, the cyber threat intelligence platform from South Korea’s AI SPERA, is unveiling a new product called Criminal IP AITEM (AI-Powered Threat Exposure Management) at GovWare 2026 in Singapore. The launch marks the company’s attempt to push Attack Surface Management (ASM) past simple asset discovery and into real-time investigation, prioritization, and response — a gap many security teams say is their biggest pain point today.
Why Criminal IP AITEM goes beyond standard ASM tools
Traditional ASM products are built to find internet-facing assets — servers, domains, IP addresses, admin panels — before attackers do. Criminal IP says that’s no longer enough on its own. “Seeing a threat and responding to it are completely different challenges,” said Byungtak Kang, CEO of AI SPERA. He argues that organizations now have more visibility than ever but still struggle to act on what they find, which is the problem Criminal IP AITEM is designed to solve by using AI to filter noise, add context, and guide investigations.
That urgency is rising because AI is also making attacks faster and easier to launch. Automated scanning, published proof-of-concept exploits, and AI-assisted vulnerability discovery let attackers find and hit exposed systems more quickly than before — a dynamic echoed in recent reporting, such as CISA Warns of Critical Gitea Vulnerability Exploited in Code Injection Attacks, where a known flaw was weaponized for code injection soon after disclosure.
What Criminal IP AITEM actually covers
AITEM pulls together exposure data from external assets, open-source intelligence, dark web sources, internal infrastructure, leaked data, “Shadow AI” usage, and emerging vulnerabilities into one view, rather than treating each as a separate tool. It’s built on Criminal IP’s existing threat intelligence — open ports, exposed services, abuse history, scanner activity, and known malicious infrastructure — so teams can see not just what’s exposed, but why it matters. That kind of context has become more important as attackers find creative entry points, similar to the session-hijacking tactics described in NovaCookies Phishing Toolkit Exploits DocuSign to Hijack Microsoft 365 Sessions.
At GovWare 2026, Kang will present a session titled “From Visibility to Threat Hunting: A Case Study of AI-Driven Attack Surface Management,” sharing real-world examples of faster investigation and response. Kang summed up the company’s bet: “The competition in ASM is no longer about who finds the most assets. It will be about who can operate faster, respond more effectively, and mobilize the organization.”
المصدر: BleepingComputer